Back to Basics: AI Security that Actually Works
Security fundamentals don't expire. They just get harder to prove.
For years, security teams have built their programs on fragmented inventories, siloed tools, and unreconciled data. That was survivable when threats moved at a human speed. AI changed the pace, and bad data feeding an AI agent doesn't just slow analysts down. It quietly becomes the wrong answer, delivered fast.
What we'll explore:
What's broken: why data quality is the real AI problem and how fragmented sources and siloed tools make AI outputs unreliable before the first query runs.
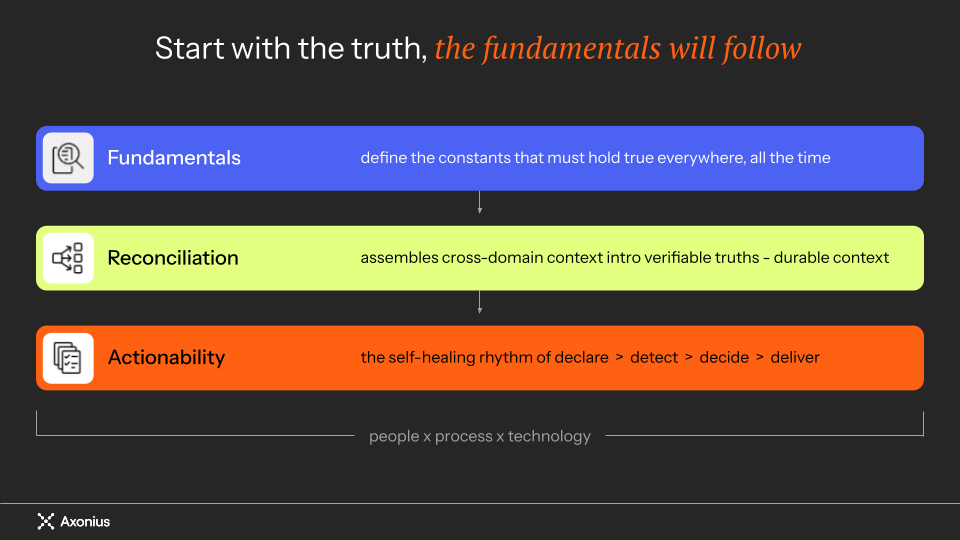
How to fix it: the self-healing loop in practice, a repeatable rhythm connecting policy to action: declare, detect, decide, deliver.
How to drive action and risk reduction: the metrics that actually matter, MTTO and verified remediation rate, and how to find the last-mile gaps where prioritization breaks down.
How to extend your fundamentals into the AI era: non-human identities, agentic guardrails, and AI asset discovery. The new basics, built on the ones that never changed.
You'll leave with a model for making AI work in security operations and the metrics to prove it's working, whether you're just starting your AI journey or trying to make existing investments defensible.